10 mag 2020

Brutality: A Fuzzer For Any GET Entries

Brutalitys' Features
  • Multi-threading on demand.
  • Fuzzing, bruteforcing GET params.
  • Find admin panels.
  • Colored output.
  • Hide results by return code, word numbers.
  • Proxy support.
  • Big wordlist.
Screenshots:

Brutality's Installtion

How to use Brutality?

Examples:
   Use default wordlist with 5 threads (-t 5) and hide 404 messages (–e 404) to fuzz the given URL (http://192.168.1.1/FUZZ):
python brutality.py -u 'http://192.168.1.1/FUZZ' -t 5 -e 404

   Use common_pass.txt wordlist (-f ./wordlist/common_pass.txt), remove response with 6969 length (-r 6969) and proxy at 127.0.0.1:8080 (-p http://127.0.0.1:8080) to fuzz the given URL (http://192.168.1.1/brute.php?username=admin&password=FUZZ&submit=submit#):
python brutality.py -u 'http://192.168.1.1/brute.php?username=admin&password=FUZZ&submit=submit#' -f ./wordlist/common_pass.txt -r 6969 -p http://127.0.0.1:8080

ToDo List:
  • Smooth output.
  • Export file report.
  • Modularization.

More articles


  1. Codigo Hacker
  2. Marketing Growth Hacking
  3. Seguridad Y Hacking
  4. Hacking Linux Distro
  5. Programas Para Hackear
  6. El Libro Del Hacker
  7. Hacking Net
  8. Hacking Google Home Mini
  9. Curso Hacker
  10. Car Hacking
  11. Hacker En Español
  12. Best Hacking Games
  13. Wifi Hacking App
  14. Hacking Team
  15. Hacking Software

15 Important Run Commands Every Windows User Should Know

There are several ways to efficiently access the files, folders, and programs in Windows operating system. We can create shortcuts, pin programs to the taskbar, Start menu shortcuts etc. but we can't do it for all programs in many cases. However, the Windows Run Command box is one of the most efficient ways of accessing system programs, folders, and settings.

In this article, I am going to share 15 most important Run commands for Windows users. These commands can make it easier to manage a lot of tasks.
How to open Windows Run command box?
You need to press Win+R (Hold Windows button then Press R)

Important Run Commands Every Windows User Should Know

1. %temp%
This is the fastest way to clear the temporary files from your computer. It can save a lot of space which was being wasted by temporary files.
2. cmd 
This command will open the windows DOS command prompt. Windows command prompt is very useful for performing many tasks which are not possible using graphical user interface.
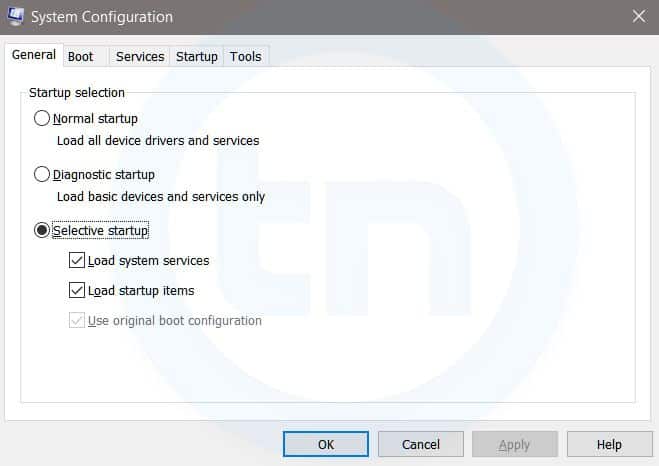
3. MSConfig
Windows Run Command - MSconfig-compressed
Windows System Configuration
This command will open Windows System Configuration where you can edit different things like the boot options, startup options, services, etc.
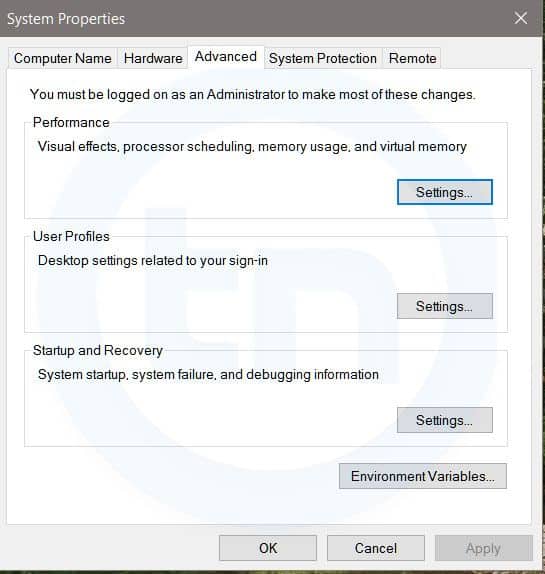
4. sysdm.cpl
Windows Run Command - sysdm cpl-compressed
System Properties window
This command will open the System Properties window, Where you can change the system protection and performance related many settings
5. Powershell
Powershell is very similar the command prompt. Just type this command in the Run dialog box, and you will have your PowerShell opened without administrator privileges.
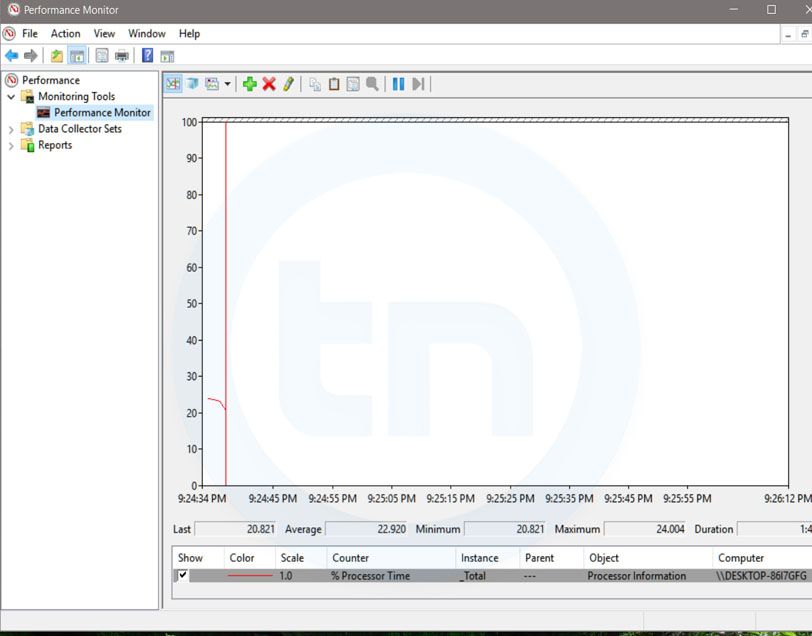
6. perfmon.msc
Windows Run Command - perfmon msc-compressed
Windows System Performance monitor
This command can be used to monitor the performance of your computer. There are plenty of options for monitoring the system performance
7. regedit
Regedit Run command is used to open the Windows Registry. It is a hierarchical database that hosts all the configurations and settings of Windows operating system, it's users and the installed software.
8. \ (Backslash)
This is one of the lesser known Run commands. Just enter the backslash into the Run dialog box and it will open up the C drive. It is one of the quickest ways to access the C drive.
9. . (Dot)
This is yet another lesser known Run command. When executed, it opens the current user's home folder which hosts all the other local folders like the Downloads, Documents, Desktop, Pictures, etc.
10. .. (Double Dots)
When you execute these two dots in the Run dialog box, it will open up the Users folder which is located directly on the C drive
11. Control
This command will open the control panel. Control panel is used for managing all the system settings and programs
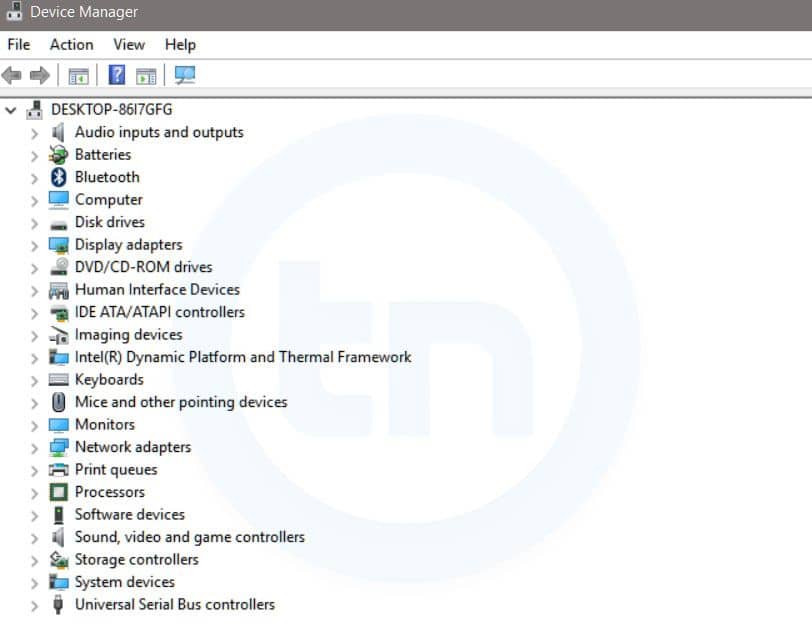
12. hdwwiz.cpl
Windows Run Command - hdwwiz-
Windows Device Manager
This command is used to open the Device Manager in Windows. You can manage all the device connected internally or externally to your PC.
13. Notepad
The quickest way to open notepad in Windows. Just type this command in Run Box and hit enter.
14. osk
This command will open On-Screen Keyboard on your display monitor. You can easily touch and type or use your mouse for typing.
15. taskmgr 
This command will open task manager where you can manage all the processes and programs running on Windows Operating system.

More articles


  1. Programas Para Hackear
  2. Python Desde 0 Hasta Hacking - Máster En Hacking Con Python
  3. Hacking Time
  4. Hacking Udemy
  5. Hacking To The Gate Lyrics
  6. Mundo Hacker
  7. Paginas De Hackers
  8. Hacking Food

Tishna: An Automated Pentest Framework For Web Servers, Web Applications To Web Security

About Tishna:
   Tishna is complete automated pentest framework for web servers, application layer to web security.

   Tishna was tested on: Kali Linux, Parrot Security OS, Black Arch, Termux, Android Led TV.


Tishna's interface: Tishna has 62 options with full automation and can be use for web security swiss knife.

Tishna's installation: First, boot your Kali Linux or Parrot Security OS up. Then open Terminal and enter these commands

Appeared:
  • Cyber Space (Computer Security).
  • Terror Security (Computer Security).
  • National Cyber Security Services.

Brief Introduction
  • Tishna is useful in Banks, Private Organisations and Ethical hacker personnel for legal auditing.
  • It serves as a defense method to find as much as information possible for gaining unauthorised access and intrusion.
  • With the emergence of more advanced technology, cybercriminals have also found more ways to get into the system of many organizations.
  • Tishna software can audit, servers and web behaviour.
  • Tishna can perform Scanning & Enumeration as much as possible of target.
  • It's first step to stop cyber criminals by securing your Servers and Web Application Security.
  • Tishna is false positive free, when there is something it will show no matter what, if it is not, it will give blank results rather error.

Developer

Support to the coder
   You can sponsor and support via BTC.
   The bitcoin address: 3BuUYgEgsRuEra4GwqNVLKnDCTjLEDfptu
qr code

More information

  1. Como Ser Hacker
  2. Paginas Para Hackear
  3. Windows Hacking
  4. Amiibo Hacking
  5. Hacking Smart Tv
  6. Elhacker Ip
  7. Grey Hat Hacking

Change Passwords Regularly - A Myth And A Lie, Don'T Be Fooled, Part 1


TL;DR: different passwords have different protection requirements, and different attackers using various attacks can only be prevented through different prevention methods. Password security is not simple. For real advise, checking the second post (in progress).

Are you sick of password advices like "change your password regularly" or "if your password is password change it to pa$$w0rd"? This post is for you!

The news sites are full of password advises nowadays due to recent breaches. When I read/watch these advise (especially on CNN), I am usually pissed off for a lot of reasons. Some advises are terrible (a good collection is here), some are good but without solutions, and others are better, but they don't explain the reasons. Following is my analysis of the problem. It works for me. It might not work for you. Comments are welcome!

Password history

Passwords have been used since ancient times.


Because it is simple. When I started using the Internet, I believe I had three passwords. Windows login, webmail, and IRC. Now I have ~250 accounts/passwords to different things, like to my smartphone, to my cable company (this password can be used to change the channels on the TV), to my online secure cloud storage, to full disk encryption to start my computer, to my nude pictures, to my WiFi router, to my cloud server hosting provider, etc etc etc. My money is protected with passwords, my communication is protected with passwords/encryption, my work is protected with passwords. It is pretty damn important. But yet people tend to choose lame passwords. Pretty lame ones. Because they don't think it can be significant. But what is not essential today will be relevant tomorrow. The service you used to download music (iTunes) with the lame password will one day protect all your Apple devices, where attackers can download your backup files, erase all your devices, etc. The seven-character and one capital rule is not enough anymore. This advice is like PDF is safe to open, Java is secure. Old, outdated, untrue.

Now, after this lengthy prologue, we will deep dive into the analysis of the problem, by checking what we want to protect, against whom (who is the attacker), and only after that, we can analyze the solutions. Travel with me, I promise it will be fun! ;)

What to protect?

There are different services online, and various services need different ways to protect. You don't use the same lock on your Trabant as you do on your BMW.

Internet banking, online money

For me, this is the most vital service to protect. Luckily, most of the internet banking services use two-factor authentication (2FA), but unfortunately, not all of them offer transaction authorization/verification with complete transactions. 2FA is not effective against malware, it just complicates the attack. Transaction authorization/verification is better, but not perfect (see Zitmo). If the access is not protected with 2FA, better choose the best password you have (long, real random, sophisticated, but we will get to this later). If it is protected with 2FA, it is still no reason not to use the best password ;) This is what I call the "very high-level password" class.


Credit card data

This system is pretty fucked up bad. Something has to be secret (your credit card number), but in the meantime that is the only thing to identify your credit card. It is like your username is your password. Pretty bad idea, huh? The problem is even worse with a lot of different transaction types, especially when the hotel asks you to fax both sides of your CC to them. Unfortunately, you can't change the password on your credit card, as there is no such thing, but Verified by VISA or 3-D Secure with 2FA might increase the chances your credit card won't get hacked. And on a side note, I have removed the CVV numbers from my credit/debit cards. I only read it once from the card when I received it, I don't need it anymore to be printed there.
And sometimes, you are your own worst enemy. Don't do stupid things like this:


Work related passwords (e.g. Windows domain)

This is very important, but because the attack methods are a bit different, I created this as a different category. Details later.

Email, social sites (Gmail/Facebook/Twitter), cloud storage, online shopping

This is what I call the "high level password" class.
Still, pretty important passwords. Some people don't understand "why would attackers put any energy to get his Facebook account?" It is simple. For money. They can use your account to spread spam all over your Facebook wall. They can write messages to all of your connections and tell them you are in trouble and send money via Western Union or Bitcoin.


They can use your account in Facebook votes. Your e-mail, cloud storage is again very important. 20 years ago you also had letters you didn't want to print and put in front of the nearest store, neither want you to do that with your private photo album. On a side note, it is best to use a cloud storage where even the cloud provider admin can't access your data. But in this case, with no password recovery option, better think about "alternative" password recovery mechanisms.

Other important stuff with personal data (e.g. your name, home address)

The "medium level password" class. This is a personal preference to have this class or not, but in the long run, I believe it is not a waste of energy to protect these accounts. These sites include your favorite pizza delivery service, your local PC store, etc.

Not important stuff

This is the category other. I usually use one-time disposable e-mail to these services. Used for the registration, get what I want, drop the email account. Because I don't want to spread my e-mail address all over the internet, whenever one of these sites get hacked. But still, I prefer to use different, random passwords on these sites, although this is the "low level password" class.

Attackers and attack methods

After categorizing the different passwords to be protected, let's look at the different attackers and attack methods. They can/will/or actively doing it now:

Attacking the clear text password 

This is the most effective way of getting the password. Bad news is that if there is no other factor of protection, the victim is definitely not on the winning side. The different attack methods are:

  • phishing sites/applications,


  • social engineering,
  • malware running on the computer (or in the browser), 
  • shoulder surfing (check out for smartphones, hidden cameras), 
  • sniffing clear-text passwords when the website is not protected with SSL,
  • SSL MiTM,
  • rogue website administrator/hacker logging clear text passwords,
  • password reuse - if the attacker can get your password in any way, and you reuse it somewhere else, that is a problem,
  • you told your password to someone and he/she will misuse it later,
  • hardware keyloggers,
  • etc.

The key thing here is that no matter how long your passwords are, no matter how complex it is, no matter how often do you change it (except when you do this every minute ... ), if it is stolen, you are screwed. 2FA might save you, or might not.

Attacking the encrypted password 

This is the usual "hack the webserver (via SQL injection), dump the passwords (with SQLMap), post hashes on pastebin, everybody starts the GPU farm to crack the hashes" scenario. This is basically the only scenario where the password policies makes sense. In this case the different level of passwords need different protection levels. In some cases, this attack turns out to be the same as the previous attack, when the passwords are not hashed, or are just encoded.

The current hash cracking speeds for hashes without any iterations (this is unfortunately very common) renders passwords like Q@tCB3nx (8 character, upper-lowercase, digit, special characters) useless, as those can be cracked in hours. Don't believe me? Let's do the math.

Let's say your password is truly random, and randomly choosen from the 26 upper, 26 lower, 10 digit, 33 special characters. (Once I tried special passwords with high ANSI characters inside. It is a terrible idea. Believe me.). There are 6 634 204 312 890 620 different, 8 character passwords from these characters. Assuming a 2 years-old password cracking rig, and MD5 hash cracking with 180 G/s speed, it takes a worst case 10 hours (average 5) to crack the password, including upgrading your bash to the latest, but still vulnerable bash version. Had the password been 10 characters long, it would take 10 years to crack with today hardware. But if the password is not truly random, it can be cracked a lot sooner.

A lot of common hashing algorithms don't use protections against offline brute-force attacks. This includes LM (old Windows hashes), NTLM (modern Windows hashes), MD-5, SHA1-2-512. These hashing algorithms were not developed for password hashing. They don't have salting, iterations, etc. out of the box. In the case of LM, the problem is even worse, as it converts the lowercase characters to uppercase ones, thus radically decreasing the key space. Out of the box, these hashes are made for fast calculation, thus support fast brute-force.


Another attack is when the protected thing is not an online service, but rather an encrypted file or crypto-currency wallet.

Attacking the authentication system online

This is what happened in the recent iCloud hack (besides phishing). Attackers were attacking the authentication system, by either brute-forcing the password, or bypassing the password security by answering the security question. Good passwords can not be brute-forced, as it takes ages. Good security answers have nothing to do with the question in first place. A good security answer is as hard to guess as the password itself. If password recovery requires manual phone calls, I know, it is a bit awkward to say that your first dog name was Xjg.2m`4cJw:V2= , but on the other hand, no one will guess that!


Attacking single sign on

This type of attack is a bit different, as I was not able to put the "pass the hash" attacks anywhere. Pass the hash attack is usually found in Windows domain environments, but others might be affected as well. The key thing is single sign on. If you can login to one system (e.g. your workstation), and access many different network resources (file share, printer, web proxy, e-mail, etc.) without providing any password, then something (a secret) has to be in the memory which can be used to to authenticate to the services. If an attacker can access this secret, he will be able to access all these services. The key thing is (again) it does not matter, how complex your passwords are, how long it is, how often do you change, as someone can easily misuse that secret.


Attacking 2FA

As already stated, 2 factor authentication raises the efforts from an attacker point of view, but does not provide 100% protection. 
  • one time tokens (SecurID, Yubikey) can be relayed in a man-in-the-middle attack, 
  • smartcard authentication can be relayed with the help of a malware to the attacker machine - or simply circumvented in the browser malware, 
  • text based (SMS) messages can be stolen by malware on the smartphone or rerouted via SS7, 
  • bio-metric protection is constantly bypassed,
  • SSH keys are constantly stolen,
  • but U2F keys are pretty good actually, even though BGP/DNS hijack or similar MiTM can still circumvent that protection,
  • etc. 


Others

Beware that there are tons of other attack methods to access your online account (like XSS/CSRF), but all of these have to be handled on the webserver side. The best you can do is to choose a website where the Bug Bounty program is running 24/7. Otherwise, the website may be full of low hanging, easy-to-hack bugs.

Now that we have covered what we want to protect against what, in the next blog post, you will see how to do that. Stay tuned. I will also explain the title of this blog post.Continue reading

Thousand Ways To Backdoor A Windows Domain (Forest)

When the Kerberos elevation of privilege (CVE-2014-6324 / MS14-068) vulnerability has been made public, the remediation paragraph of the following blog post made some waves:
http://blogs.technet.com/b/srd/archive/2014/11/18/additional-information-about-cve-2014-6324.aspx

"The only way a domain compromise can be remediated with a high level of certainty is a complete rebuild of the domain."

Personally, I agree with this, but .... But whether this is the real solution, I'm not sure. And the same applies to compromised computers. When it has been identified that malware was able to run on the computer (e.g. scheduled scan found the malware), there is no easy way to determine with 100% certainty that there is no rootkit on the computer. Thus rebuilding the computer might be a good thing to consider. For paranoids, use new hardware ;)

But rebuilding a single workstation and rebuilding a whole domain is not on the same complexity level. Rebuilding a domain can take weeks or months (or years, which will never happen, as the business will close before that).

There are countless documented methods to backdoor a computer, but I have never seen a post where someone collects all the methods to backdoor a domain. In the following, I will refer to domain admin, but in reality, I mean Domain Admins, Enterprise Admins, and Schema Admins.


Ways to backdoor a domain

So here you go, an incomplete list to backdoor a domain:

  • Create a new domain admin user. Easy to do, easy to detect, easy to remediate
  • Dump password hashes. The attacker can either crack those or just pass-the-hash. Since KB2871997, pass-the-hash might be trickier (https://technet.microsoft.com/library/security/2871997), but not impossible. Easy to do, hard to detect, hard to remediate - just think about service user passwords. And during remediation, consider all passwords compromised, even strong ones.
  • Logon scripts - modify the logon scripts and add something malicious in it. Almost anything detailed in this post can be added :D
  • Use an already available account, and add domain admin privileges to that. Reset its password. Mess with current group memberships - e.g. http://www.exploit-db.com/papers/17167/
  • Backdoor any workstation where domain admins login. While remediating workstations, don't forget to clean the roaming profile. The type of backdoor can use different forms: malware, local admin, password (hidden admin with 500 RID), sticky keys, etc.
  • Backdoor any domain controller server. For advanced attacks, see Skeleton keys 
  • Backdoor files on network shares which are commonly used by domain admins by adding malware to commonly used executables - Backdoor factory
  • Change ownership/permissions on AD partitions - if you have particular details on how to do this specifically, please comment
  • Create a new domain user. Hide admin privileges with SID history. Easy to do, hard to detect, easy to remediate - check Mimikatz experimental for addsid
  • Golden tickets - easy to do, hard to detect, medium remediation
  • Silver tickets - easy to do, hard to detect, medium/hard remediation
  • Backdoor workstations/servers via group policy
    • HKEY_LOCAL_MACHINE\ Software\ Microsoft\ Windows\ CurrentVersion\ RunOnce,
    • scheduled tasks (run task 2 years later),
    • sticky-keys with debug
  • Backdoor patch management tool, see slides here
[Update 2017.01.10]


Other tricks

The following list does not fit in the previous "instant admin" tips, but still, it can make the attackers life easier if their primary foothold has been disabled:

  • Backdoor recent backups - and when the backdoor is needed, destroy the files, so the files will be restored from the backdoored backup
  • Backdoor the Exchange server - get a copy of emails
  • Backdoor workstation/server golden image
  • Change permission of logon scripts to allow modification later
  • Place malicious symlinks to file shares, collect hashes via SMB auth tries on specified IP address, grab password hashes later
  • Backdoor remote admin management e.g. HP iLO - e.g. create new user or steal current password
  • Backdoor files e.g. on shares to use in SMB relay
  • Backdoor source code of in-house-developed software
  • Use any type of sniffed or reused passwords in new attacks, e.g. network admin, firewall admin, VPN admin, AV admin, etc.
  • Change the content of the proxy pac file (change browser configuration if necessary), including special exception(s) for a chosen domain(s)  to use proxy on malicious IP. Redirect the traffic, enforce authentication, grab password hashes, ???, profit.
  • Create high privileged users in applications running with high privileges, e.g. MSSQL, Tomcat, and own the machine, impersonate users, grab their credentials, etc. The typical pentest path made easy.
  • Remove patches from servers, change patch policy not to install those patches.
  • Steal Windows root/intermediate CA keys
  • Weaken AD security by changing group policy (e.g. re-enabling LM-hashes)
Update [2015-09-27]: I found this great presentation from Jakob Heidelberg. It mentions (at least) the following techniques, it is worth to check these:
  • Microsoft Local Administrator Password Solution
  • Enroll virtual smart card certificates for domain admins

Forensics

If you have been chosen to remediate a network where attackers gained domain admin privileges, well, you have a lot of things to look for :)

I can recommend two tools which can help you during your investigation:

Lessons learned

But guess what, not all of these problems are solved by rebuilding the AD. One has to rebuild all the computers from scratch as well. Which seems quite impossible. When someone is creating a new AD, it is impossible not to migrate some configuration/data/files from the old domain. And whenever this happens, there is a risk that the new AD will be backdoored as well.

Ok, we are doomed, but what can we do? I recommend proper log analysis, analyze trends, and detect strange patterns in your network. Better spend money on these, than on the domain rebuild. And when you find something, do a proper incident response. And good luck!

Ps: Thanks to Andrew, EQ, and Tileo for adding new ideas to this post.

Check out the host backdooring post as well! :)

Related news


9 mag 2020

Hidden Networks: Nueva Versión Para Detectar Redes Ocultas En Tu Empresa

Ha pasado ya algo de tiempo desde que publicamos aquí la primera versión de esta prueba de concepto llamada Hidden Networks. Como recordaréis, su idea principal (la cual está desarrollada en profundidad en este paper) es controlar y hacer un seguimiento de aquellos dispositivos (en principio pendrives USB) que se han conectado en algún equipo dentro de nuestra infraestructura.

Figura 1: Hidden Networks: Nueva versión para detectar redes ocultas en tu empresa

De esta forma, podríamos visualizar esas conexiones entre equipos que incluso, en principio, podrían estar incluso desconectados de la red. Después de la charla que dimos en la C0r0n4CON (y que Pablo González resumió en este post), queremos compartir con vosotros esta nueva versión que incorpora algunas mejoras.


Hidden Networks (HN) nos ayuda a implementar desde un enfoque práctico y automatizar esta tarea de identificación, permitiendo analizar esa información tanto en un equipo local, como en todos los que tengamos acceso desde el equipo anfitrión (desde el cual estamos lanzando la aplicación). Es decir, si estamos en un dominio, podríamos auditar todos los equipos dentro del mismo desde HN.

Figura 3: Hidden Networks (HN) en ElevenPaths

En esta nueva versión de HN (0.9b), hemos realizado mejoras y limpieza del código (aún así queda mucho por hacer) y añadido nuevas funcionalidades, sobre todo a la hora de dibujar el grafo o la red. De todas formas, aún tenemos mucho que mejorar, implementar y optimizar, pero lo realmente importante de HN es su concepto principal (que Chema Alonso ya publicó originalmente aquí), su filosofía de trazar y dibujar esas redes que en principio, no son visibles.

Figura 4: Nuevo diseño de la interfaz de Hidden Networks

Como hemos comentado antes, las principales mejoras se han centrado a la hora de dibujar la red o grafo, así como la identificación del dispositivo USB. Una vez hemos terminado nuestro análisis completo recopilando los datos desde la red, o simplemente importando un CSV (generado con HN o incluso manualmente, para pruebas) directamente con el botón "Plot single CSV", podemos proceder a dibujar la red sin necesidad de crear un proyecto previo. Pero esta vez, además el grafo se ha mejorado sensiblemente.


Figura 5: Presentación de Hidden Networks en C0r0n4con

Ahora, además de dibujar aquellos nodos que se encuentran una red (color azul claro) se destacan también aquellos nodos que están totalmente aislados de la red (con color naranja). Es decir, podemos detectar de un golpe de vista aquellos que estaban sin conexión, pero en los cuales se ha conectado el pendrive. De esta forma, queremos resaltar el punto clave de este análisis: los equipos que no tienen conexión a la red y su conexión (o red oculta) con el resto.

Figura 6: Ejemplo de grafo que muestra una red oculta trazada por un
pendrive USB, destacando los nodos sin conexión o aislados (naranja)

En el grafo mostrado en la Figura 6, podemos comprobar la trazabilidad marcada, en este caso, por un pendrive USB de la marca Toshiba. Vemos que la primera conexión se realizó en la dirección IP 198.168.1.30 a las 14:30 del día 9/1/2017 y partir de aquí comienza su movimiento a través de diferentes imágenes, incluso con otras direcciones IP como por ejemplo en el quinto salto, donde vemos la dirección IP 10.1.1.15. Durante la traza podemos ver que también accede a un equipo llamado PCINSOLATED_018 el día 14/6/2017. Es decir, en este equipo se ejecutó HN a nivel local y recopiló esta información dentro del mismo proyecto.

De esta forma podemos comprobar cómo se ha realizado una conexión entre equipos, digamos "conectados" y otros totalmente aislados. Después de visitar este nodo aislado, vemos que conecta con otro que esta vez sí tiene conectividad (aquí podríamos haber recopilado la información HN tanto en remoto o en local). Finalmente perdemos la trazabilidad en un equipo también aislado. Si hemos sufrido algún tipo de incidente en nuestra organización, HN nos muestra un nuevo punto de vista de análisis para poder detectar su origen y movimiento por nuestra infraestructura y así ayudarnos a su identificación y mitigación.

Figura 7: Ejemplo de grafo e identificación del dispositivo USB

Otra de las nuevas funcionalidades que hemos implementado es la identificación visual del dispositivo USB. Basándonos en la marca y modelo obtenidos durante la auditoría, podemos realizar una búsqueda por Internet de las imágenes de dicho dispositivo para de esta forma, tener una referencia visual del mismo.

Esta imagen nos puede ayudar a la hora de recopilar aquellos USB sospechosos de realizar la infección en las máquinas para su posterior análisis, ya estén aisladas o conectadas a la red. Por lo tanto, junto al grafo mostramos también una fotografía de dicho dispositivo junto a su identificador único, el número de serie o Serial ID (como se puede apreciar en la Figura 7).

Figura 8: Ejemplo de informe generado en PDF de HN

Finalmente, hemos mejorado también la generación de informes en PDF con toda la información recopilada durante el análisis. En ella se incluyen los datos del dispositivo (como el USB Serial Id, USB Name, etcétera) así como la trazabilidad completa de los saltos realizados. También se incluyen el grafo y la imagen del dispositivo USB.

Por cada elemento detectado (USB) se realiza un informe individual con toda esta información. De esta forma cerramos todos los pasos que HN pretende demostrar en una PoC, los cuales empiezan por una adquisición de los datos (tanto en red como local), análisis de los mismos (trazabilidad utilizando las fechas y hora de la primera inserción), dibujo del grafo dirigido (marcando los nodos aislados) y finalmente, un informe donde se detalla y resume toda la información obtenida.

Figura 9: Fichero CSV encargado de dibujar parte del grafo de la Figura 6,
donde podemos ver la información almacenada (nombre de equipo,
dirección IP, descripción, Serial ID y fecha/hora de inserción)

Pero mejor vamos a ver esta nueva versión de HN en acción. En el vídeo a continuación hemos creado el siguiente escenario. Existe un dominio llamado testdomain.local gestionado por un servidor de Windows Server 2016, donde se incluyen dentro del mismo otros tres equipos más, dos con Windows 7 y uno con Windows 10.

Lanzaremos HN desde uno de los equipos con Windows 7 (pantalla principal). A partir de este punto veremos todo el proceso de adquisición de datos a través de la red de los equipos a auditar y finalmente veremos el dibujo del grafo, así como la información de los USB. Al final del vídeo también se muestra cómo se importa un CSV (el que aparece en la Figura 9) para dibujar un grafo más completo donde se pueden comprobar nodos sin conexión aparente (aislados).

Figura 10: Demo de la nueva versión de Hidden Networks

Insistimos, Hidden Networks es una prueba de concepto donde se pueden mejorar muchas de sus funcionalidades, así como el código. Pero nuestra intención no es hacer una aplicación totalmente funcional al 100%, sino trasladaros de una manera práctica, el concepto de las redes ocultas y su posible utilidad dentro del mundo del pentesting o incluso del Análisis Forense. De todas formas, haremos un esfuerzo e intentaremos mejorar y actualizar la aplicación siempre que sea posible. Puedes acceder a toda la información, así como al código fuente en este enlace.

Happy Hacking Hackers!!!

Autores:

Fran Ramírez, (@cyberhadesblog) es investigador de seguridad y miembro del equipo de Ideas Locas en CDO en Telefónica, co-autor del libro "Microhistorias: Anécdotas y Curiosidades de la historia de la informática (y los hackers)", del libro "Docker: SecDevOps", también de "Machine Learning aplicado a la Ciberseguridad" además del blog CyberHades. Puedes contactar con Fran Ramirez en MyPublicInbox.


 Contactar con Fran Ramírez en MyPublicInbox

Read more
  1. Hacking Roblox
  2. Curso De Ciberseguridad Y Hacking Ético
  3. Hacking Tools
  4. Hacking Videos
  5. Tutorial Hacking
  6. Herramientas Hacking
  7. Aprender Hacking Etico
  8. Hacking Hardware

This Asia-Pacific Cyber Espionage Campaign Went Undetected For 5 Years

An advanced group of Chinese hackers has recently been spotted to be behind a sustained cyber espionage campaign targeting government entities in Australia, Indonesia, Philippines, Vietnam, Thailand, Myanmar, and Brunei—which went undetected for at least five years and is still an ongoing threat. The group, named 'Naikon APT,' once known as one of the most active APTs in Asia until 2015,

via The Hacker News

Related links